
Kişisel Veri Güvenliği Rehberi (Teknik ve İdari Tedbirler)
Kişisel Verileri Koruma Kurumu (KVKK)
KVKK's April 2025 guide on the technical and administrative measures that data controllers should take under Article 12 of Law No. 6698.
On this page
Overview
This guide was published by the Personal Data Protection Authority (KVKK) in April 2025 as KVKK Publication No. 72. It describes the technical and administrative measures data controllers should take to meet the security obligation in Article 12 of Law No. 6698. The guide can be read freely on the Authority's website; copying and distribution require permission, so this library cites it only.
The guide treats administrative measures (Section 2) and technical measures (Section 3) separately, with summary tables in Section 4. The topics covered include risk identification, staff training, data minimisation, processor management, cyber security, monitoring, physical security of media and server rooms, cloud storage, system procurement and backups. The document thus turns the legal obligation into concrete control items. The summary tables make it easy to use the measures as a checklist.
For data centre design, the most directly relevant parts are those on physical security and the cloud. Physical environments holding personal data should be protected against external risks such as fire and flood, with controlled entry and exit. Servers, backup devices and media should be moved to a room with extra security, kept locked and have entry and exit logged.
For cloud storage, the controller is expected to assess the provider's security, encrypt the data, use separate keys per cloud service where possible and destroy keys when the service ends. Regular vulnerability scans and penetration tests, log collection and formal incident reporting procedures are also expected. The guide gives no measurable thresholds; the level of measures is set by risk analysis.
Key points
- The guide separates administrative measures (Section 2) and technical measures (Section 3), with summary tables in Section 4.
- Physical environments holding personal data should be protected against external risks such as fire and flood, with controlled entry and exit (3.3, p. 23).
- Servers, backup devices and media should be moved to an extra-secure room, kept locked, with entry and exit logged (3.3, p. 24).
- For cloud storage, the controller must assess provider security; data should be encrypted, with separate keys per service where possible, and keys destroyed when the service ends (3.4, pp. 25-26).
- Regular vulnerability scans and penetration tests, log collection and formal incident reporting procedures are expected (3.2, p. 22).
- The guide is dated April 2025 and published as KVKK Publication No. 72.
- Related references: Law No. 6698 Article 12, ISO/IEC 27001, ISO/IEC 22237-6.
Using it in design
- When the 'personal data hosted' flag is set, require locked server rooms with access logging, fire and flood protection and segregated backup storage rooms in the layout checklist.
- Encrypt tenant data at rest with per-environment keys.
- Document key destruction when a contract ends.
- Include penetration testing, vulnerability scanning and log collection in operating procedures.
Monthly newsletter · free
Keep your reading list current
Once a month: new library sources, changes to Turkish regulations and upcoming data centre events.
SoSo CAD
Bring standards pre-checks into your project
Review model-based TS EN 50600 and Tier pre-checks, missing inputs and items requiring engineering review in SoSo CAD.
Request a demo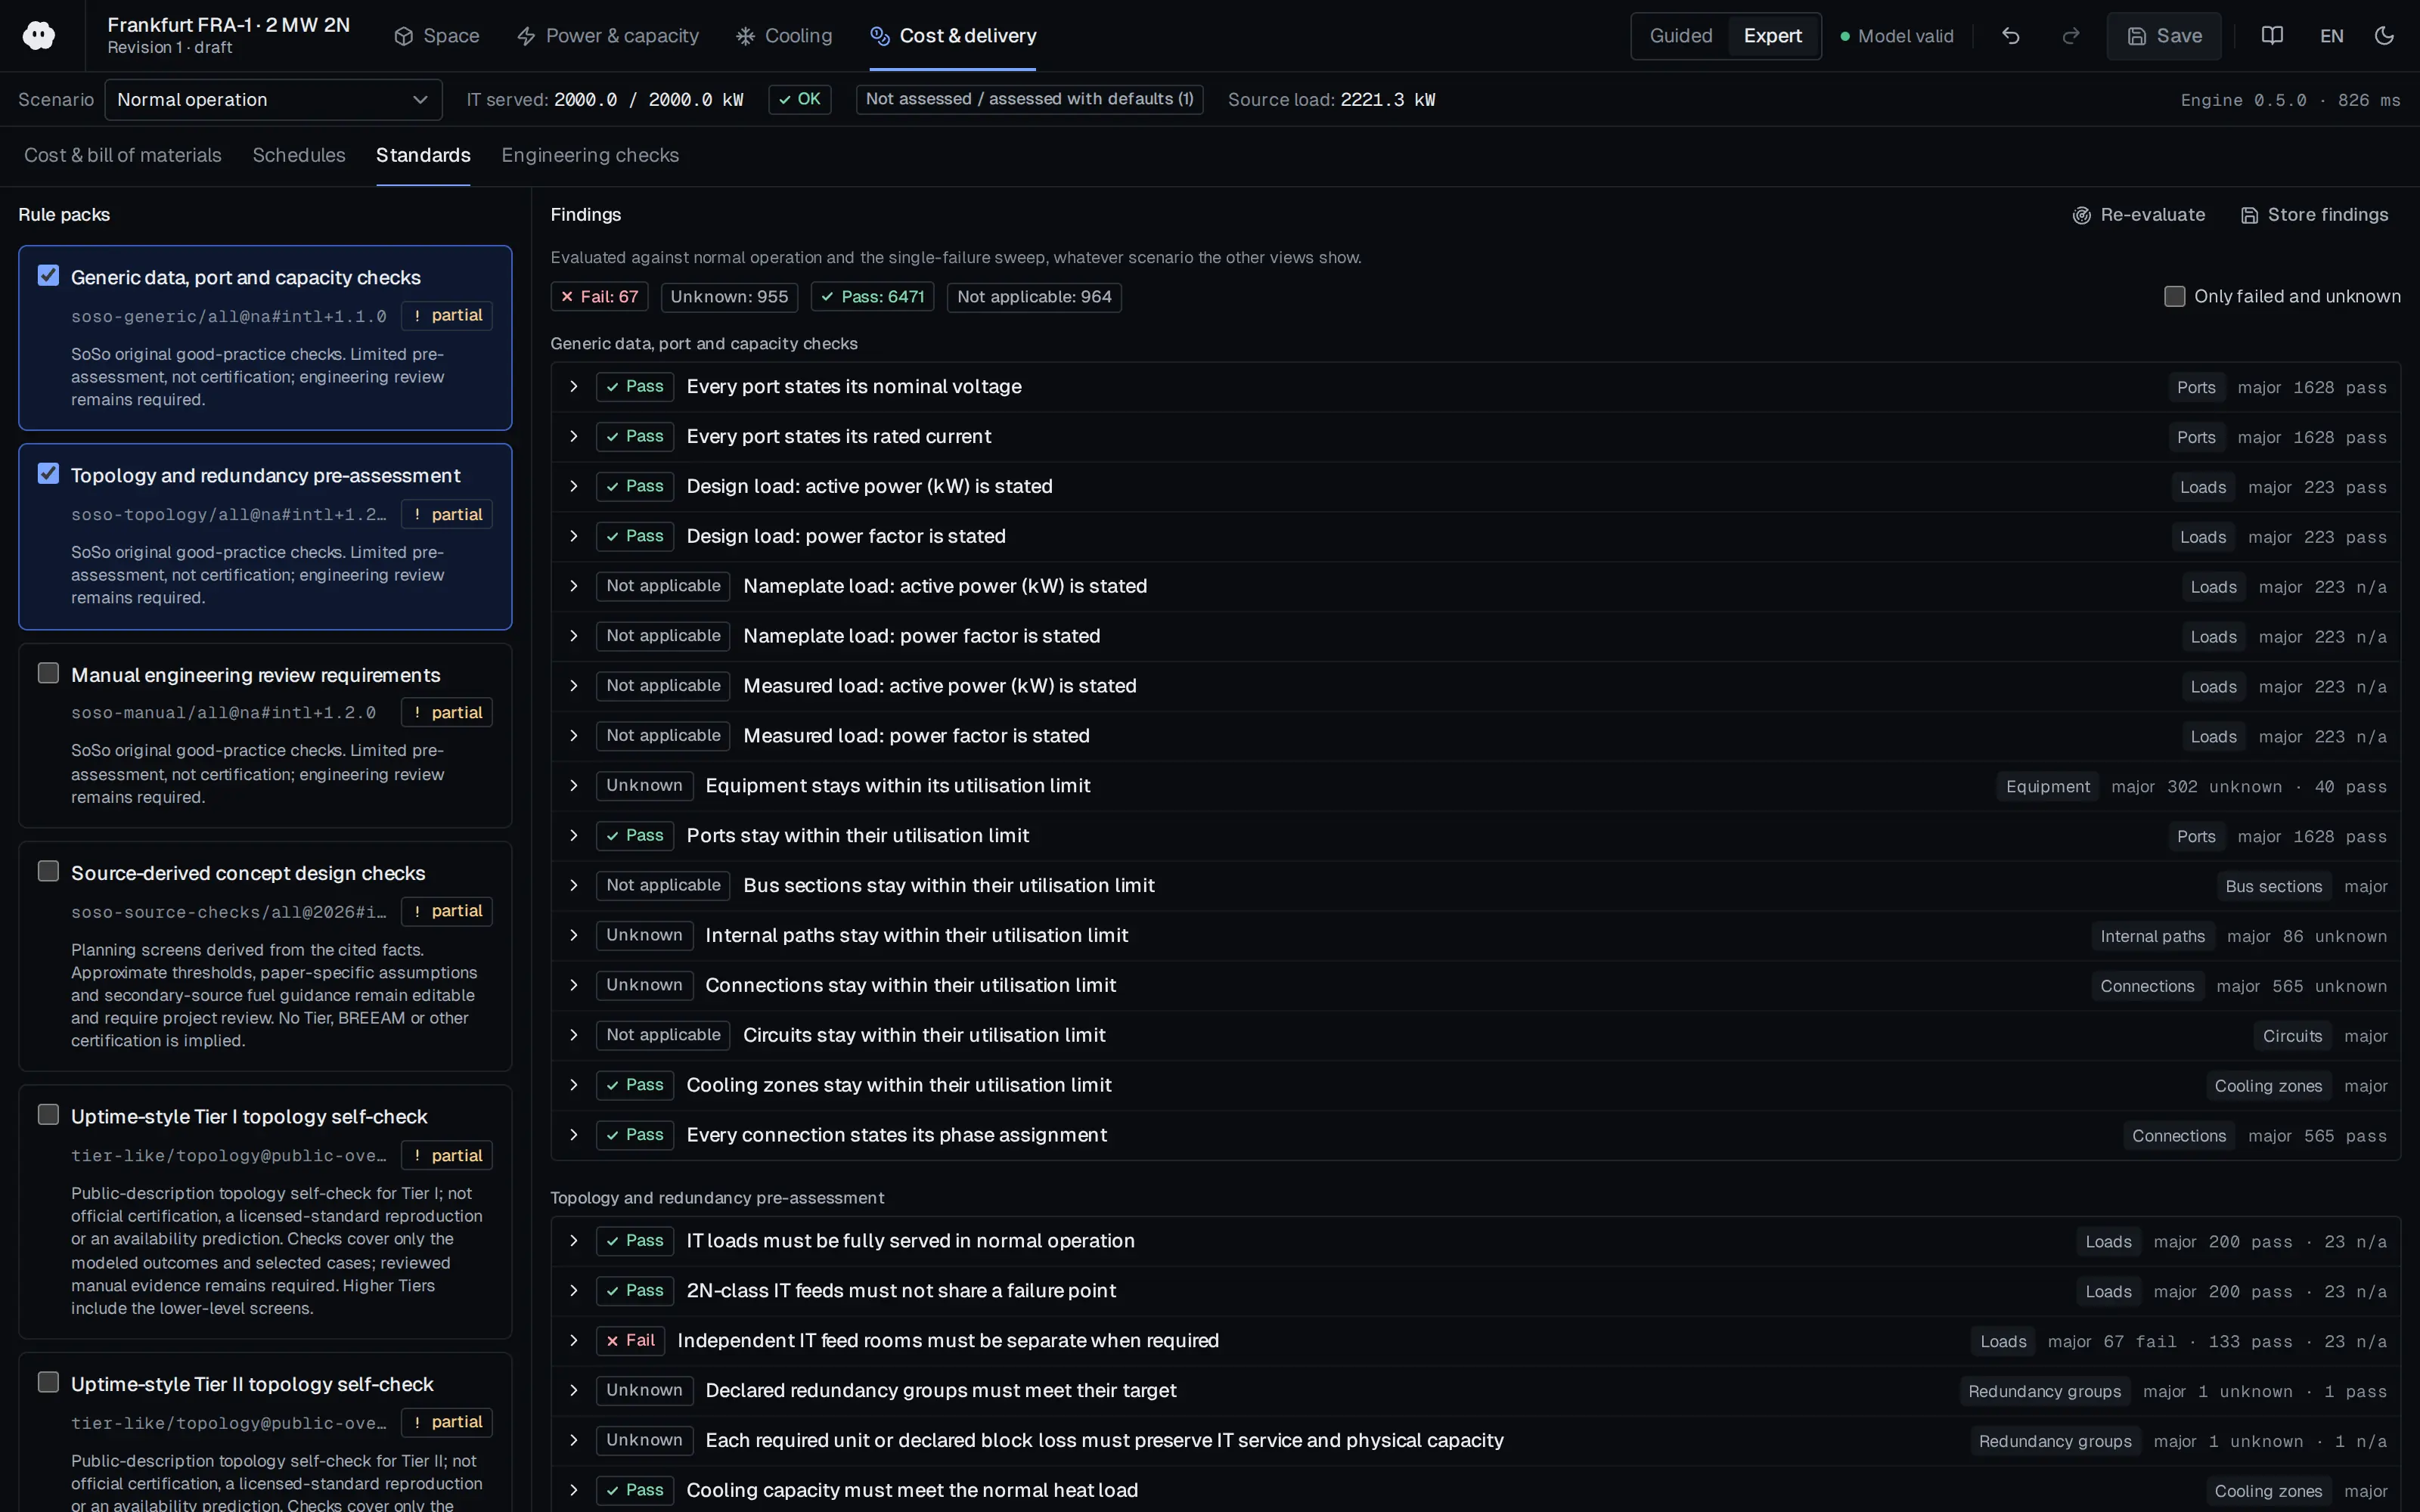
Who should read it
Engineers, security officers and compliance teams designing and operating data centres that hold personal data.
Related standards
- 6698 sayılı Kanun Madde 12
- ISO/IEC 27001
- ISO/IEC 22237-6
Publication details
- Authors
- Kişisel Verileri Koruma Kurumu (KVKK)
- Publisher
- Kişisel Verileri Koruma Kurumu (KVKK)
- Year
- 2025
- Document number
- KVKK Yayınları No: 72
- Document language
- Turkish
- Source type
- Turkish regulation
- Access
- Free to read
- Licence
- Copyright retained; citation only — the publisher’s terms apply to the original document
Original licence note
KVKK publication; the booklet states that copying, reproduction or distribution beyond personal use without permission is prohibited (FSEK 5846). Citation only; PDF not redistributed.
Citation
Kişisel Verileri Koruma Kurumu (KVKK) (2025). Kişisel Veri Güvenliği Rehberi (Teknik ve İdari Tedbirler). Kişisel Verileri Koruma Kurumu (KVKK). KVKK Yayınları No: 72. https://www.kvkk.gov.tr/SharedFolderServer/CMSFiles/7512d0d4-f345-41cb-bc5b-8d5cf125e3a1.pdf
Events on this subject
Browse the events calendarAll content and rights belong to the respective authors and publishers. SoSo CAD provides only the citation, its own summary and a link to the source, and is not responsible for the sources' content.
Related sources
All sources on this topicKişisel Verileri Koruma Kurumu (KVKK) 2017
Kişisel Verilerin Silinmesi, Yok Edilmesi veya Anonim Hale Getirilmesi Hakkında Yönetmelik (Regulation on Deletion, Destruction or Anonymisation of Personal Data)
Implement scheduled purge or anonymisation jobs with a configurable interval not exceeding six months, including backups.
- Resmî Gazete 30224, 28.10.2017.
National Institute of Standards and Technology 2024
The NIST Cybersecurity Framework (CSF) 2.0
Create separate Organizational Profiles for a facility's IT, OT and building management systems (for example electrical and cooling SCADA/BMS) and state each Profile's scope.
- The Core has 22 Categories with Subcategories; the outcomes are not a checklist.
Türkiye Büyük Millet Meclisi 2016
Law No. 6698 on the Protection of Personal Data (KVKK)
Product/deployment: offer TR-region or on-prem hosting so Turkish customers avoid Article 9 transfers.
- The law was amended in 2024 by Law 7499.
Kişisel Verileri Koruma Kurumu (KVKK) 2025
Guide on Transferring Personal Data Abroad (Kişisel Verilerin Yurt Dışına Aktarılması Rehberi)
Treat any foreign-located support engineer's remote session into a Turkish customer's SoSo CAD instance or DCIM as a transfer and gate it behind a standard-contract check.
- Guide published January 2025 as KVKK Publication No. 48.
Kişisel Verileri Koruma Kurumu (KVKK) 2024
Regulation on the Procedures and Principles for the Transfer of Personal Data Abroad (Kişisel Verilerin Yurt Dışına Aktarılmasına İlişkin Usul ve Esaslar Hakkında Yönetmelik)
If SoSo CAD uses foreign sub-processors (cloud, email, monitoring), maintain an unmodified KVKK standard contract for each transfer path.
- Standard contracts are published by the Board and must be used without modification (Article 14(2)-(3)).
Kişisel Verileri Koruma Kurumu (KVKK) 2017
Regulation on the Data Controllers Registry (Veri Sorumluları Sicili Hakkında Yönetmelik)
For customers who self-host SoSo CAD, generate a VERBİS-ready inventory (purposes, data categories, recipients, foreign transfers, security measures) from the product's data-processing configuration.
- For legal persons the controller is the legal entity itself (Article 11).