
Law No. 6698 on the Protection of Personal Data (KVKK)
Original title 6698 sayılı Kişisel Verilerin Korunması Kanunu
Türkiye Büyük Millet Meclisi
Turkey's personal data protection law (consolidated with the 2024 amendments by Law 7499), setting data-security duties for controllers, the public registry and a tiered regime for cross-border transfers.
On this page
Overview
Law No. 6698 on the Protection of Personal Data was published in Official Gazette no. 29677 of 7 April 2016. This page rests on the text consolidated with the 2024 amendments made by Law 7499. The law sets data-security duties for controllers and processors, the public Data Controllers Registry and a tiered regime for cross-border transfers. It governs both data centres hosting personal data and SoSo CAD's own SaaS hosting.
Transfers abroad are covered by Article 9. A transfer is allowed where a processing condition exists and an adequacy decision covers the country, sector or organisation; adequacy is reviewed at least every four years. Without adequacy, appropriate safeguards are needed: non-treaty agreements, Board-approved binding corporate rules, Board-published standard contracts, or Board-approved written undertakings. Standard contracts must be notified to the Authority within five working days of signature.
Data security is addressed in Article 12: controllers must take all technical and administrative measures to prevent unlawful processing and access and to safeguard data, and they are jointly responsible with processors. Controllers register in the public Data Controllers Registry before processing, unless exempted by Board criteria. Both provisions make documented measures and clear processor contracts part of the compliance picture.
Article 18 sets administrative fines. Data security failures carry fines of 15,000 to 1,000,000 TL and failure to notify standard contracts 50,000 to 1,000,000 TL; these are the base amounts in the Law text. The text is official legislation, so current amounts and wording should be taken from mevzuat.gov.tr. Related documents include the Regulation on Transfers Abroad, the Personal Data Security Guide, GDPR and ISO/IEC 27001. Together these provisions make security design and contractual arrangements with processors a legal matter, not just a technical choice.
Key points
- Transfers abroad need a processing condition and an adequacy decision; adequacy is reviewed at least every four years (Article 9(1)-(2)).
- Without adequacy: appropriate safeguards such as non-treaty agreements, Board-approved BCRs, Board-published standard contracts or Board-approved written undertakings (Article 9(4)).
- Standard contracts must be notified to the Authority within five working days of signature (Article 9(5)).
- Controllers must take all technical and administrative measures and are jointly responsible with processors (Article 12(1)-(2)).
- Controllers register in the public Data Controllers Registry before processing unless exempted (Article 16(1)-(2)).
- Fines: data security failures 15,000-1,000,000 TL; failure to notify standard contracts 50,000-1,000,000 TL (Article 18(1)(b),(d)).
- The law was amended in 2024 by Law 7499.
Using it in design
- Product/deployment: offer TR-region or on-prem hosting so Turkish customers avoid Article 9 transfers.
- If any processing or support access is abroad, track a standard-contract notification task.
- In data-centre design, expose a 'personal data hosted' flag that raises physical-security and access-logging defaults.
- Document technical and administrative measures (access control, logging, backup) in contracts with processors.
Monthly newsletter · free
Keep your reading list current
Once a month: new library sources, changes to Turkish regulations and upcoming data centre events.
SoSo CAD
Bring standards pre-checks into your project
Review model-based TS EN 50600 and Tier pre-checks, missing inputs and items requiring engineering review in SoSo CAD.
Request a demo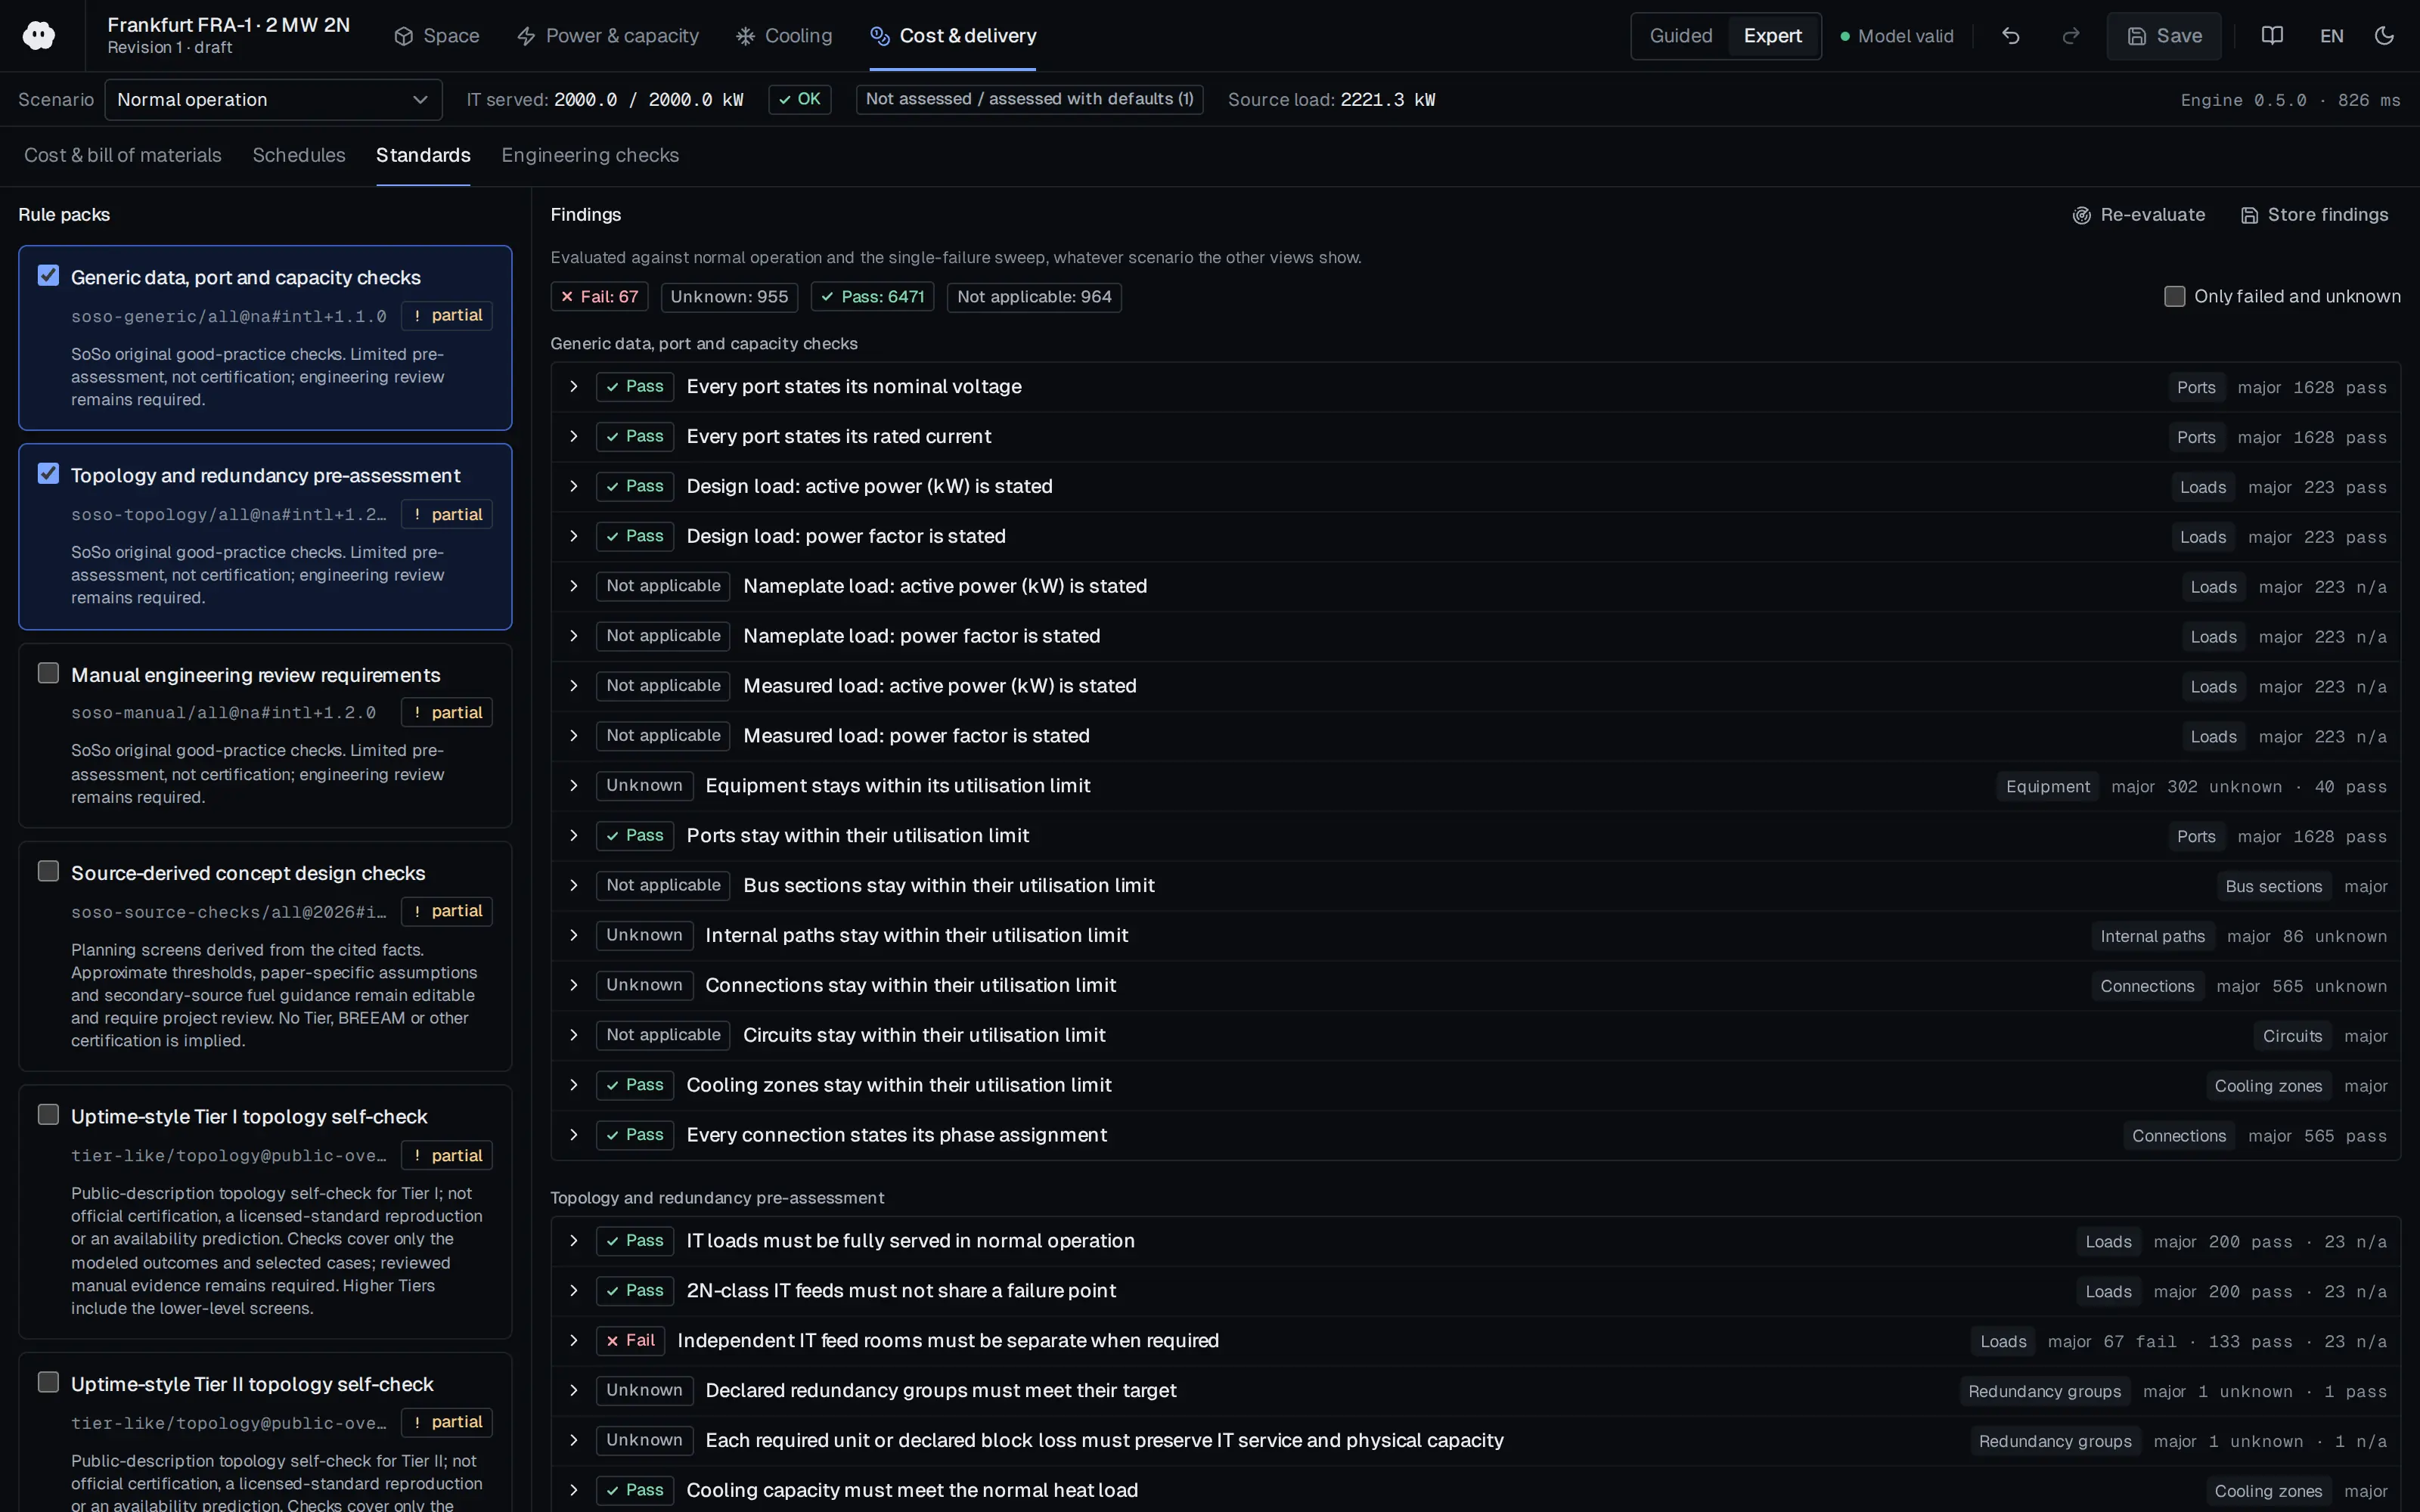
Who should read it
Data center owners hosting personal data, SaaS providers, legal and compliance teams, and security designers.
Related standards
- KVKK Yurt Dışına Aktarım Yönetmeliği
- Kişisel Veri Güvenliği Rehberi
- GDPR (EU) 2016/679
- ISO/IEC 27001
Publication details
- Authors
- Türkiye Büyük Millet Meclisi
- Publisher
- Türkiye Büyük Millet Meclisi
- Year
- 2016
- Document number
- Kanun No. 6698 (RG 29677, 07.04.2016)
- Document language
- Turkish
- Source type
- Turkish regulation
- Access
- Free to read
- Licence
- Bibliographic reference only — the document is not redistributed here; confirm reuse terms at the original source
Original licence note
Official Turkish legislation published in the Resmî Gazete; FSEK (Law 5846) Art. 31 makes laws and regulations freely reproducible, but this library keeps it citation-only by policy. Text read from mevzuat.gov.tr (consolidated version as of 2026-11).
Citation
Türkiye Büyük Millet Meclisi (2016). 6698 sayılı Kişisel Verilerin Korunması Kanunu. Türkiye Büyük Millet Meclisi. Kanun No. 6698 (RG 29677, 07.04.2016). https://www.mevzuat.gov.tr/mevzuat?MevzuatNo=6698&MevzuatTur=1&MevzuatTertip=5
Events on this subject
Browse the events calendarAll content and rights belong to the respective authors and publishers. SoSo CAD provides only the citation, its own summary and a link to the source, and is not responsible for the sources' content.
Related sources
All sources on this topic
National Institute of Standards and Technology 2024
The NIST Cybersecurity Framework (CSF) 2.0
Create separate Organizational Profiles for a facility's IT, OT and building management systems (for example electrical and cooling SCADA/BMS) and state each Profile's scope.
- The Core has 22 Categories with Subcategories; the outcomes are not a checklist.
Kişisel Verileri Koruma Kurumu (KVKK) 2025
Kişisel Veri Güvenliği Rehberi (Teknik ve İdari Tedbirler)
When the 'personal data hosted' flag is set, require locked server rooms with access logging, fire and flood protection and segregated backup storage rooms in the layout checklist.
- The guide is dated April 2025 and published as KVKK Publication No. 72.
Kişisel Verileri Koruma Kurumu (KVKK) 2017
Kişisel Verilerin Silinmesi, Yok Edilmesi veya Anonim Hale Getirilmesi Hakkında Yönetmelik (Regulation on Deletion, Destruction or Anonymisation of Personal Data)
Implement scheduled purge or anonymisation jobs with a configurable interval not exceeding six months, including backups.
- Resmî Gazete 30224, 28.10.2017.
Türkiye Büyük Millet Meclisi 2025
Law No. 7545 on Cyber Security (7545 sayılı Siber Güvenlik Kanunu)
When the client is public-sector or critical infrastructure, flag that security systems (access control, CCTV, network security appliances) must come from authorised suppliers.
- The Presidency may audit, including on-site inspections (Article 8).
Türkiye Büyük Millet Meclisi 2007
Law No. 5627 on Energy Efficiency (5627 sayılı Enerji Verimliliği Kanunu)
In the operations/energy module, compute annual energy in TEP (toe) from the energy model.
- Related instruments: the related regulations and ISO 50001.
National Institute of Standards and Technology 2025
NIST SP 800-88 Rev. 2: Guidelines for Media Sanitization
Add media sanitization to the facility's storage and server lifecycle plan at commissioning, and label media with the confidentiality category of the system.
- Cryptographic erase: at least 128 bits of security strength, key sanitization by ISO/IEC 19790 zeroization, ECB mode not allowed.